Travel agents have been urged to look out for unusual website activity and check their technology providers have applied security fixes following a worldwide cybersecurity alert.
Two flaws in the PHP programming software, which underpins an estimated 70% of websites, were identified by US cybersecurity researchers using AI tools, having previously gone undetected.
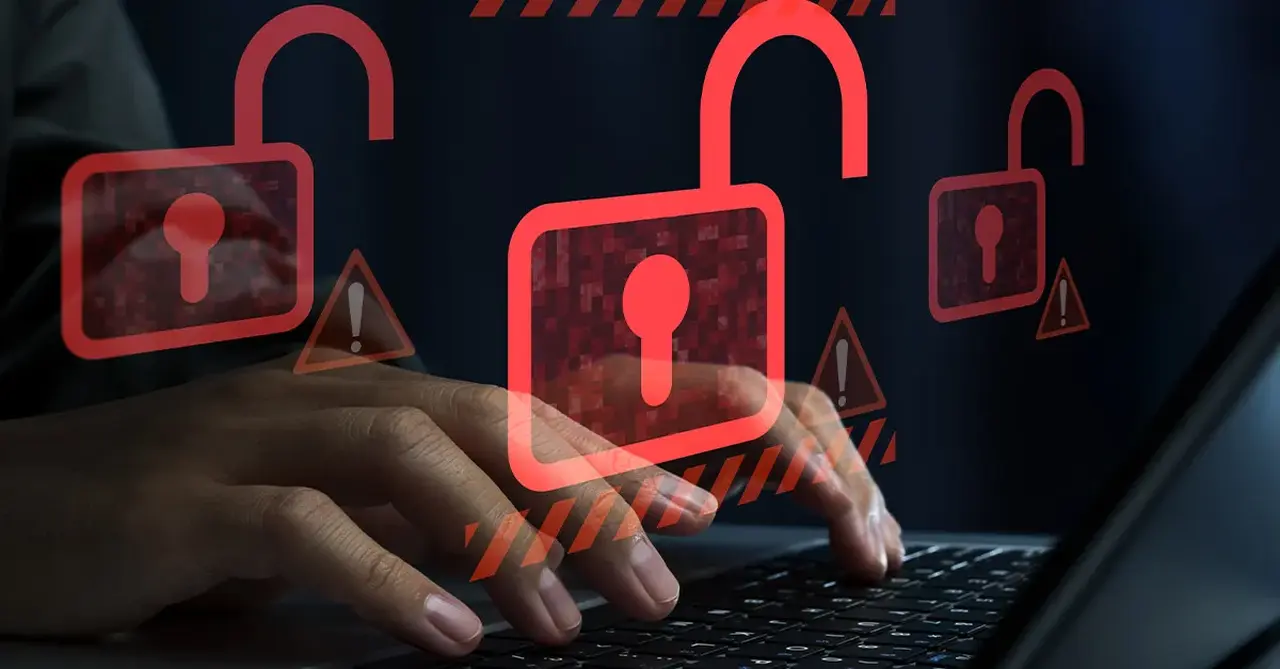
The flaws could allow hackers to take control of websites and servers without needing login credentials. More than 30 UK government websites were taken offline following the alert.
Advantage Travel Partnership issued a warning to members, noting the “security vulnerabilities” could allow attackers “to run malicious commands on affected servers”.
Simply Cruises co-founder Chris Hughes, who has a background in software, described the risks as “pretty much at the highest level” and compared the impact to “having the lock broken on the front door of your shop”.
Abta said the issue “is not affecting abta.com” and told Travel Weekly: “We haven’t received any reports of members being affected or contacting us for support.”
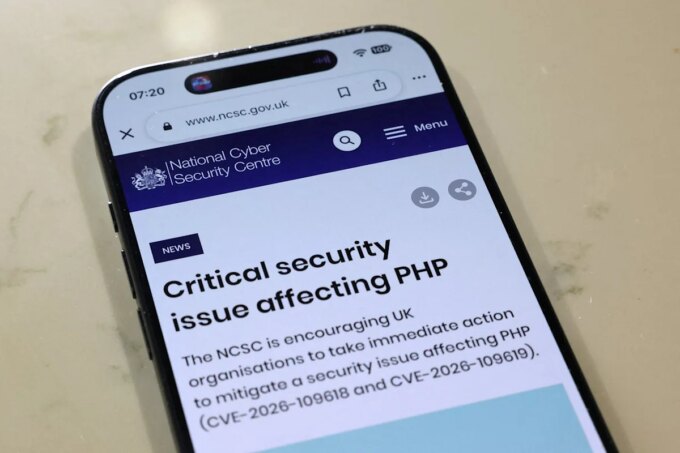
However, the UK National Cyber Security Centre warned of “a critical security issue that may allow attackers to execute commands on any web server running PHP” and advised: “Organisations using any version of PHP should update to the latest fixed version [or] consider taking the system offline”.
Advantage reassured members using its Advantage Website Solution they were not affected and advised others to “contact your website hosting provider or developer to confirm whether your website uses PHP and whether the necessary security updates have been applied”.
It warned members to “remain alert for unusual activity”.
Hughes said: “It’s crucial companies are on top of this.” But he added: “Travel is the worst industry when it comes to tech. It’s so behind on everything. A lot of companies don’t have in-house development teams and are reliant on third-party companies to update their software.”
He noted the fix involves patching the software, but said: “This is not as easy as updating an app. There are various versions of PHP out there [and companies may] need to move to a new version. It’s not as easy as clicking ‘update’. Depending how old your technology stack is, you might need to bring forward updating it all.”
Hughes said Simply Cruises became aware of the problem immediately “because we subscribe to technology security lists”, adding: “We patched all Simply Cruises systems and checked them throughout the day and night.”
He warned: “There have not been stories about this being exploited yet, but that will happen.”
James Brightley, chief technology officer at travel CRM software company TProfile, said: “We did a full audit even though we were confident we weren’t affected.”
He noted: “Most agents buy their software from a provider. Their question should be: Do we use PHP? Do our suppliers use it? Have they communicated ‘we’re OK’? You want reassurance from providers that everything is in hand.”
Brightley added: “We came out with comms first thing to say, ‘Don’t worry, our applications are not affected.’ I hope a lot of technology suppliers did.”


Leave a comment