
Picture:
ANP/Alamy
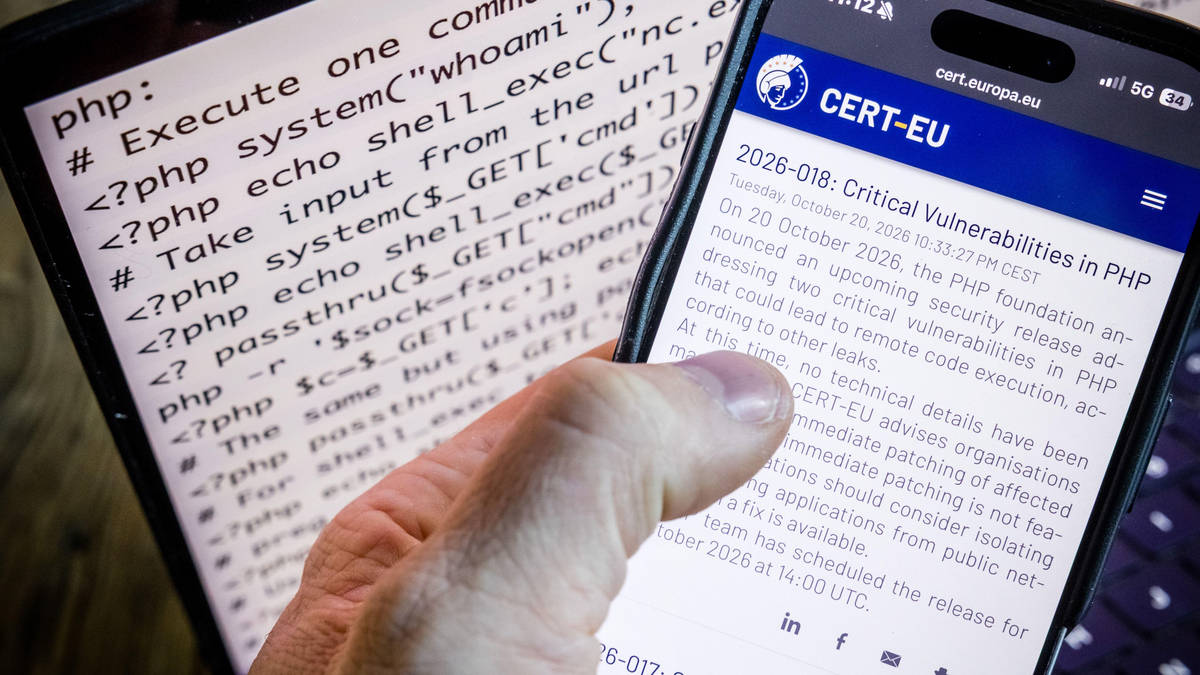
Britain’s cyber security agency has warned organisations to consider taking websites and online services offline if they cannot protect them against two critical security flaws.
The National Cyber Security Centre (NCSC) has urged UK organisations to prepare for emergency updates to software used to run websites around the world, amid fears hackers could exploit the weaknesses to break into their systems.
Fixes are due to be released at 3pm BST on Wednesday, October 21, although they could arrive earlier.
The NCSC warned: “Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated.”
The flaws affect PHP, software that works behind the scenes to keep websites running, including those built using popular platforms such as WordPress.
European cyber officials have warned that the weaknesses could allow hackers to run their own commands on vulnerable systems without needing to log in. Full details of the flaws and which versions are affected have yet to be published.
The warning means some website owners could face having to temporarily take their services offline while they wait for protection to be put in place.
Read more: Cyber attacks: Which UK companies have recently been targeted by hackers?
Read more: Chinese spies targeting UK government and military staff on job websites, warns MI5

Picture:
LBC
Cloudflare’s chief technology officer, Dane Knecht, said the company was already seeing early attacks and was updating its firewall protections.
“We are seeing early attacks emerging and are updating mitigations as new vectors show up. This is a STOPGAP only. Patch as soon as PHP releases the update,” he wrote on X.
For website owners, updating the website itself may not be enough. WordPress security company Wordfence warned that automatic WordPress updates would not install the PHP fix, advising owners to establish who is responsible for updating the software on their servers.
CERT-EU has also urged organisations unable to apply fixes immediately to consider isolating affected internet-facing applications from public networks. It said versions dating back to PHP 5 could be affected, although PHP’s developers had yet to publish a definitive list of vulnerable versions.
The PHP security team said full details of the vulnerabilities, affected versions and fixes would be published alongside the release. It also warned that updates could arrive ahead of schedule if details became public or evidence of active exploitation emerged.



Leave a comment