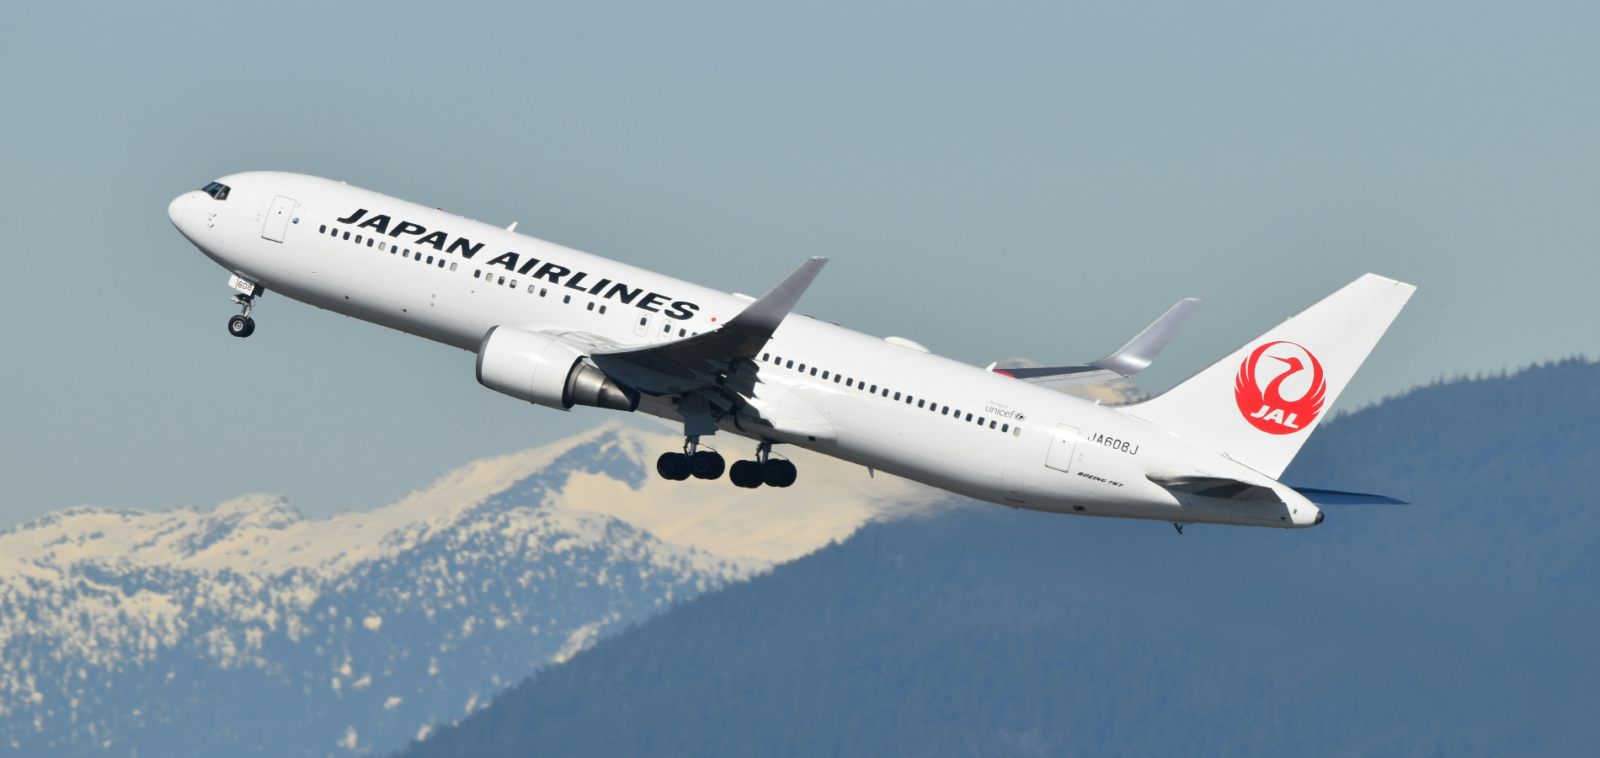
A cyber security breach at global travel technology provider Amadeus has exposed tens of thousands of airline reservations across Asia, with Japan Airlines confirming customer data was accessed and Qantas probing whether its own bookings were caught up in the incident.
Amadeus, which supplies technology to airlines, hotels and car hire companies worldwide, said it had addressed a vulnerability that allowed unauthorised access to certain booking information. Investigations into the incident remain under way.
Amadeus Finds No Evidence of Financial Data Access
The New Straits Times reported on 2 November 2026 that Amadeus had strengthened its monitoring and detection capabilities after taking steps to address the security vulnerability.
‘Although our investigations continue, we can confirm that there is no evidence that payment or financial data was accessed,’ the company said.
Amadeus said the vulnerability exposed certain data held within its booking environment. Its statement distinguishes the reservation information made accessible from financial records, for which investigators have found no evidence of access.
It also said it was in direct contact with customers and relevant authorities as it continued investigating the incident.
Qantas Investigates Its Booking Exposure
Qantas confirmed the incident to NewsWire, according to News.com.au, and said it was working with Amadeus to establish the potential impact on Qantas reservations. The spokesperson also identified Japan Airlines, All Nippon Airways (ANA), Cathay Pacific and Korean Air among the airlines involved.
Amadeus told Qantas that it had contained the issue in September. Qantas said its own systems and databases remained secure and unaffected.
The Australian airline has notified the Australian Cyber Security Centre and the Office of National Cyber Security.
Cathay Pacific Reports 53,000 Affected Bookings
In its own press release, Cathay Pacific said approximately 53,000 bookings were affected by unauthorised access to Amadeus’s system between August 2023 and September 2026.
Most affected records contained passengers’ names, booking references and flight details. A smaller group potentially included additional personal information, such as email addresses, telephone numbers, travel document details or frequent flyer numbers.
Cathay Pacific said the unauthorised party used login credentials assigned to an Amadeus system account. Amadeus notified the airline on 28 October 2026 and supplied further information the following day.
The airline added that Amadeus’s containment measures included a password reset and enhanced monitoring. Amadeus had found no evidence that the affected information had been misused.
Meanwhile, its systems and operations remained unaffected. It informed the relevant authorities and is analysing information from Amadeus before contacting affected customers individually.
Japanese and Korean Airlines Disclose Exposure
The Business Times reported that Japan Airlines Group disclosed that approximately 92,000 customers of Japan Airlines and Japan Transocean Air were affected.
ANA Holdings also announced exposure, with around 37,800 passengers’ information reportedly leaked. These figures refer to customers or passengers, whereas Cathay Pacific’s figure represents bookings.
Korean Air and Asiana Airlines issued alerts on 23 October after Amadeus notified them on 20 October, according to The Business Times. Neither carrier disclosed how many customers were affected, and both said no secondary damage had been reported at that point.
Malaysia Airlines Warns Customers About Suspicious Messages
Malaysia Airlines said in a statement dated 31 October 2026 that the incident may have affected customer information processed through Amadeus between August 2023 and September 2026.
The carrier said its own information technology systems had not been compromised and that there was no evidence of financial information being accessed.
It is working with Amadeus and other relevant parties to investigate the incident and assess its impact on customers.
As a precaution, the airline urged passengers to watch for suspicious or unsolicited communications, particularly messages seeking personal or financial information. It said it would provide further updates as more information became available.


Leave a comment