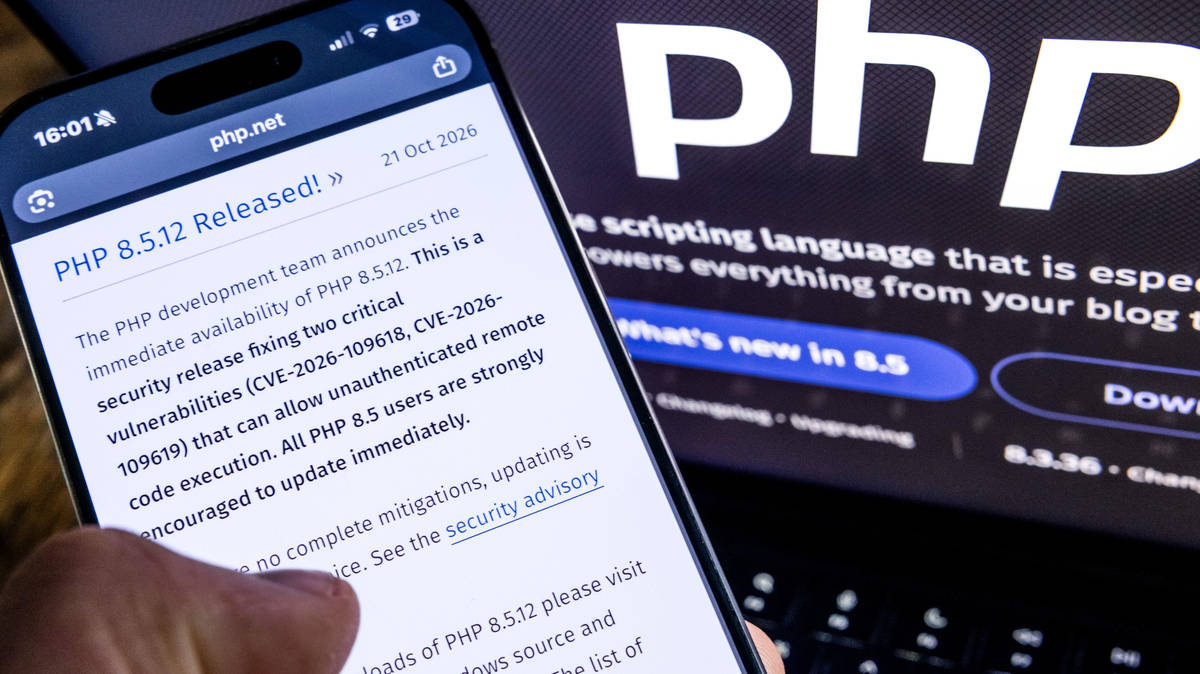
The security issue identified by the researcher could allow attackers to remotely control any web servers running the widely used programming language, PHP.

Picture:
ANP/Alamy
Hundreds of major websites around the world have been shut down after criminal hackers attempted to exploit a “critical” security flaw first identified by AI agents.
Described as “the most severe flaw in software history” by OpenAI, the technology firm that runs ChatGPT, the security issue led to websites including Oxford City Council, City of Edinburgh Council, and the Dutch Parliamentary website being taken offline.
On Tuesday, Downing Street said “limited” Government services may temporarily be offline while work is carried out to address potential PHP cyber security issues.
Hundreds of other sites were similarly taken down as a precaution, after hackers and bots attempted to exploit the cyber-security flaw.
Thirty-two Government services are offline and four are partially unavailable amid the PHP cyber security issue, a minister has said in the House of Lords.
No large UK public-facing critical services have been affected, a No 10 spokeswoman said.
OpenAI has claimed that over the past two months, it has been leading a team of researchers to address the flaw in the PHP – a type of programming language.
The company, whose AI agents have recently hacked sites including Hugging Face and Australian and US government sites, said it had supported its developers as it led the way with fixes.
The company described the incident as “one of the most impactful security issues in recent memory”, adding that while AI can help to uncover issues, it is often also employed by criminals to attack sites.
It’s thought that “millions” of attempts have been made to exploit the vulnerability.
“Our work has begun with OpenAI and NCSC to fix vulnerabilities in government systems,” a spokesperson for No. 10 said.
“No large public facing services affected, some smaller services down for update, but not hacked.”
A number of government and business websites across the world went offline on Wednesday as a security measure, after an urgent software update was issued over vulnerabilities in PHP – a programming language used extensively across the internet.
In light of the hack, a minister confirmed that the security of next week’s Government Budget has not been compromised.
Scotland Secretary Douglas Alexander was asked whether the issues identified with PHP could result in major Budget leaks because the Office for Budget Responsibility (OBR) had to take down its website.
Around 70% of websites are thought to be impacted.
The Office for Budget Responsibility also said it had followed guidance to take its website offline, “in view of the critical security issues affecting PHP”.
The developers of PHP said a set of new updates fixing two previously identified critical vulnerabilities was now live, and strongly encouraged users to update software immediately.
Cloudflare CEO Matthew Prince wrote on X: “Two classes extremely bad cyber vulnerabilities disclosed in the last 24 hours. The first potentially impacts everyone online. The second impacts nearly everyone running a server.”
In another post, he wrote: “In the 10 hours before it was publicly announced, across the Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.”
It comes as a UK government spokesperson urged “all organisations, private and public, large and small” to follow guidance in a bid to mitigate security threats to their systems.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
— Matthew Prince 🌥 (@eastdakota) October 22, 2026
The security issue identified by the researcher could allow attackers to remotely control any web servers running the widely used programming language, PHP.
PHP is used by almost 70% of websites, according to cybersecurity firm Cloudflare, and underpins popular platforms such as WordPress and Magento.
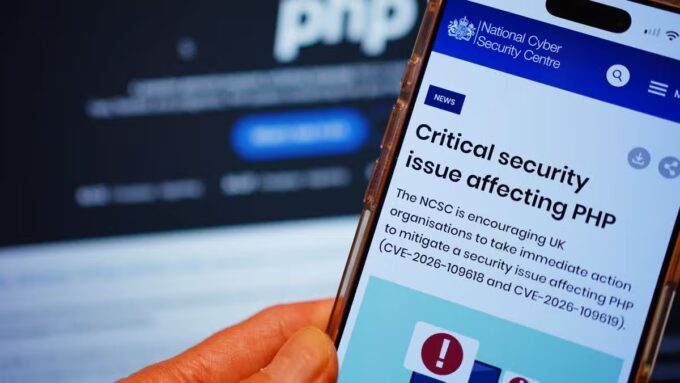
Organisations have been urged by the National Cyber Security Centre (NCSC) to update to a new, fixed version of the software.
If software cannot be immediately upgraded, organisations should consider taking their websites offline, the NCSC said.
A Government spokesperson said on Wednesday: “Work is already under way across Government to actively identify and patch any potential exposure.
“We encourage all organisations, private and public, large and small, to follow guidance issued by the NCSC to understand their exposure and take the necessary actions to safeguard their systems.”

Picture:
ANP/Alamy
The cyber division of the National Security Agency in the US warned weaknesses in the software could provide “a direct path to the server’s file system or database”.
The Wall Street Journal reported that the flaw was discovered in August by Ryan Austin, a researcher at the cybersecurity company Calif, using an advanced AI model developed by OpenAI.
PHP developers had reportedly planned a security update on Thursday, but the release was brought forward after details of its work to address the vulnerabilities leaked online.
OpenAI, which runs ChatGPT, said in the past two months it has been leading a team of researchers working to address the critical flaw in PHP, and supported its developers as it led the fixes.
The company described the incident as “one of the most impactful security issues in recent memory”, adding that while AI can help to uncover issues, it can also aid attackers.
“To our knowledge, frontier AI found these vulnerabilities before attackers did, opening a defender’s window for maintainers and security providers to prepare fixes and protections ahead of disclosure,” it said.


Leave a comment