Home Artificial intelligence Beyond Prompt Injection: The Hidden AI Security Threats in Machine Learning Platforms
Artificial intelligence

Beyond Prompt Injection: The Hidden AI Security Threats in Machine Learning Platforms

Share


Organizations should implement robust AI security frameworks that include regular testing for adversarial attacks, secure AI training pipelines with data validation, and continuous monitoring of AI model behavior in production. Essential mitigation strategies involve maintaining human oversight over critical AI applications, implementing input validation to prevent injection attacks, and establishing incident response procedures specifically for AI security threats. Additionally, companies must ensure proper access controls for AI systems and regularly update their AI tools to address emerging threats and vulnerabilities.
Source link

Leave a comment

Leave a Reply

Your email address will not be published. Required fields are marked *

Related Articles
Artificial intelligence

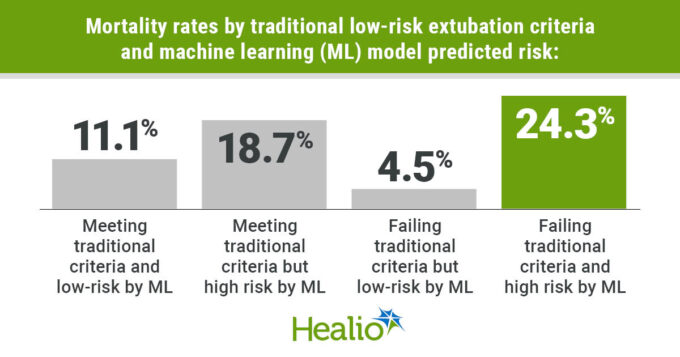
Machine learning finds patients with high-risk extubation failure

October 19, 2026 4 min read Add topic to...

Artificial intelligence

Intel seeks FCC exemption for foreign robotic equipment amid ban

Intel has asked the Federal Communications Commission for an expedited waiver. The...

Artificial intelligence

SpaceX stock may stay flat through 2027 despite 92% revenue growth and AI expansion

SpaceX, Elon Musk’s space and technology company, made history in June with...

Artificial intelligence

AI Proved the Quasi-Riemann Hypothesis. What Happens Now?

Among the 377 results that OpenAI announced on October 6, 2026, one...