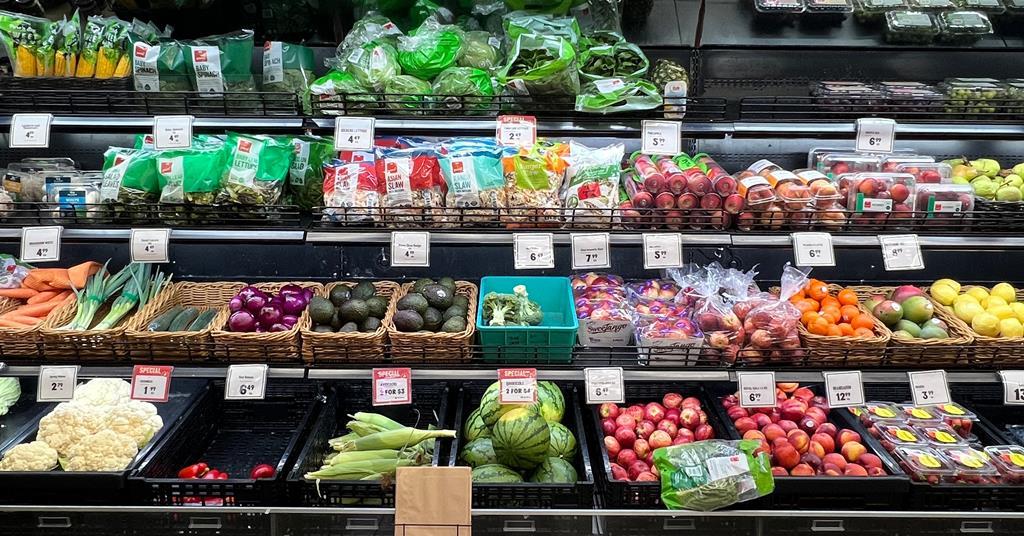
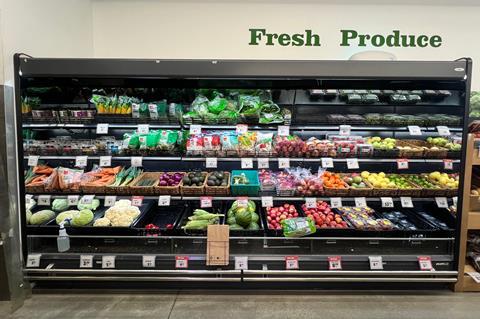
The UK fresh produce sector has left itself open to cyberattacks that target refrigeration systems, FPJ has learned.
Speaking after a spate of such attacks across several countries in Europe, Phil Pluck, chief executive of the Cold Chain Federation, urged businesses to operate on the assumption that “the next attack is a matter of when, not if”.
He also warned that recent incidents could be a precursor to a larger, more organised campaign in the run-up towards Christmas.
FPJ also understands that at least one major UK retailer has identified vulnerabilities among its cold-chain partners – such as importers and distribution partners – and urged them to take action.
The concerns follow reports that organic fruit and vegetable wholesaler Langridge Organic recently had six of its ten cold room control systems hacked, amid a wave of cyberattacks that targeted supermarket refrigeration systems in countries including Ireland, Belgium, Germany, Finland, Italy, Netherlands, Portugal and Sweden in early November.
Pluck raised concerns that Russian cybercriminal groups could be involved, potentially with links to state-sponsored activity.
Meanwhile, the National Cyber Security Centre has said that it is aware of “a couple of instances where vulnerable technology has been exploited in the UK”.
It said it was actively investigating incidents alongside international partners but declined to comment publicly on attribution.
Warning of “a larger-scale crisis”
Pluck said cybercriminals had recognised the strategic importance of the cold chain, describing it as a “constricted” and “focused” part of the food supply network where attacks could have an immediate and widespread impact.
He warned of “a larger-scale crisis that has yet to hit our cold chain industry and food supply industry”.
While hackers used to target large companies directly, Pluck said they were increasingly turning their attention to their suppliers, potentially exploiting older refrigeration systems that use open internet connections rather than secure virtual private networks (VPNs).
He added that weaknesses in existing authentication systems were leaving parts of the fresh produce cold supply chain exposed.
One anonymous source at a major UK supermarket chain told FPJ that poor security measures on refrigeration systems – including passwords based on the day’s date – had made them particularly vulnerable.
“It wasn’t really hacking. [The fridges] were hard-coded to rotate their admin password every day to the day’s date. So it was trivial to log in and fiddle with the controls at scale,” they said.
Pluck stressed that cybercriminals were increasingly sophisticated, well-resourced organisations, rather than opportunistic hackers.
He also highlighted the growing threat of “social engineering”, citing a recent incident in which hackers allegedly infiltrated a supplier before impersonating its IT department to trick an employee into granting remote access to the company’s systems.
The attackers reportedly remained undetected within the network for three weeks, waiting for an opportunity to cause disruption.
Call to bolster secuity measures
The Institute of Grocery Distribution (IGD) said that the recent attack affecting European retailers exploited vulnerabilities in connected refrigeration control systems, many of which it said were running outdated software or exposed to the public internet.
Toby Pickard, retail futures senior partner at IGD, said: “The issue is often not the latest technology itself, but legacy systems, outdated firmware, poor visibility of connected devices and insufficient cybersecurity governance.
“The lesson is not to stop connecting stores, but to ensure resilience is designed into them from the outset,” Pickard added.
Pluck urged businesses to urgently strengthen their cybersecurity by reviewing authentication procedures, introducing two-factor or multi-factor authentication, securing refrigeration systems through VPN connections and ensuring all software patches and upgrades are installed.
He also advised companies operating older equipment to contact manufacturers to establish whether systems needed to be reset to factory settings or otherwise secured.
The warnings come after UK Cyber Defence published evidence in September that identified more than 800 internet-exposed refrigeration and building-management controllers in the UK whose management interfaces were accessible directly from the public internet.
These span manufacturers Danfoss, Carel, Copeland and others, whose products are used in supermarkets and cold store distribution centres.
The centre described the figures as “a floor rather than a ceiling”, suggesting the number of potentially exposed systems could be higher.


Leave a comment