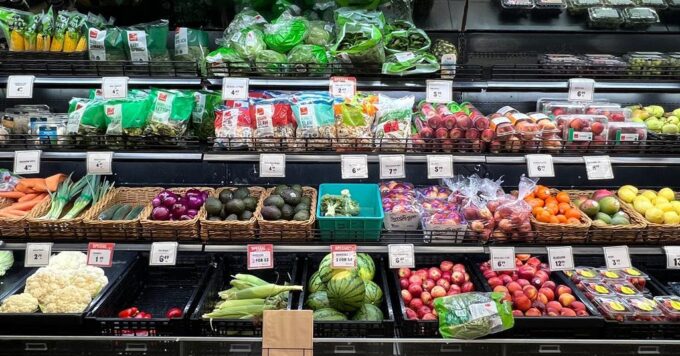
British food firms were affected by a major cyber attack that targeted freezers in supermarkets across Europe, a top security chief has confirmed.
At least seven countries have been targeted by the suspected cyber-terrorists, who raised temperatures in chillers to as high as 55C (131F).
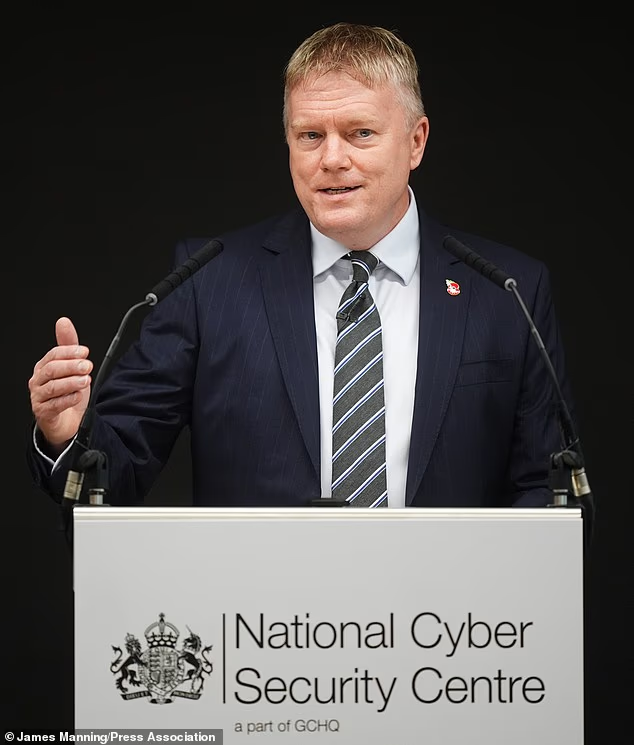
Dr Richard Horne, head of the National Cyber Security Centre (NCSC) – which is part of GCHQ – claimed ‘vulnerable technology’ in the UK had been ‘exploited’ during the hack.
Security sources have told the Daily Mail that only a small number of companies in the UK had been affected. It’s understood no major supermarkets have been hit.
A fruit and vegetable wholesaler in London affected by the hack narrowly avoided catastrophe after disconnecting their fridges from the internet, severing the attack.
Dr Horne said: ‘We don’t know the full impact, but we can see there are a couple of instances where vulnerable technology has been exploited, and we will be working with those organisations to understand more.’
He added it was ‘too early for us to say’ or to ‘give a definitive answer’ about who was behind the cyber-hack.
Dozens of shops in Belgium, Sweden, Ireland, Luxembourg and Estonia have already been targeted – just weeks after hackers turned up the temperatures of cooling units in hundreds of French grocery stores.
The latest hack involved fridges manufactured by Belgian firm Sabcobel. The company said units’ evaporators were switched to defrost mode, causing temperatures to spike from -27C (-17F) to 50C (122F) in some cases, ruining tons of meat.

Dr Richard Horne, head of the National Cyber Security Centre, said UK firms had been affected by the European supermarket freezer hack

Employees had to throw away bags of spoiled food at an ICA supermarket in Sweden
It is similar to the method used in last month’s attack on French supermarkets, which led to millions of euros’ worth of food being thrown away and even caused some small fires.
The hacks affected fridges supplied by Danfoss, which also works with British supermarkets including Tesco and Sainsbury’s.
Around 40 Delhaize and Colruyt supermarkets in Belgium and Luxembourg were hit, along with 15 Carrefour stores.
Tony Goodger, of the British group Association of Independent Meat Suppliers (Aims), claimed that a few of his 300 members had ‘unexpectedly become collateral’ during the European hack, with fridges heating up overnight.
One meat supply firm saw reportedly saw its cold units rise to up to 100C (212F) while another two claimed their units had started to defrost.
However, because of the way that abattoirs are typically run, the units were empty at the time – so there was no impact on any food produce, Aims said.
Langridge Organic, a fruit and vegetable wholesaler in London, was targeted but managed to prevent the attack from escalating after staff unplugged its cold storage units from the internet.
Alex Pearce, managing director of the company, said hackers had tried to set the six units to defrost at 150C for more than four hours before quick-thinking staff intervened. No produce was lost.
‘It clearly must have been easy to get in [to the system] because the simple solution was to unplug ourselves from the internet,’ he said.
He added the company used the same fridge control system, developed by American software firm Copeland, which was involved in the French supermarket incidents.
Dr Horne told BBC Radio 4’s Today programme: ‘It’s not just supermarkets, it’s through the whole food supply chain, and we’ve been working through the night alerting organisations where we can see they’ve got exposed technology that’s vulnerable in this way.
‘So there are handfuls of organisations in the UK we’ve alerted and we’re aware of a couple of impacts.’

An employee cleans fridges that had been hacked at an ICA store in Stockholm
An NCSC official told the Daily Mail: ‘We are aware of a small number of UK organisations that may be affected by this incident as a result of vulnerabilities on their systems, and the NCSC is supporting those that may be impacted.
‘We continue to liaise with our international partners and the affected sectors to understand and mitigate its impact.’
News of the incident came as Dr Horne warned in a speech today that Britain was facing a moment of ‘enormous consequence’ for cyber-security.
The UK has got away with doing ‘tech on the cheap’ for decades, he said, as the NCSC’s annual report suggests Britain faced being bombarded by AI-powered attacks on critical national infrastructure in the next two years.
Hackers demanding ransom payments are ‘highly likely’ to use the technology to target the UK by 2028 and hostile states such as Russia and China will routinely use the technology to pursue their goals by then, the report found.
In a speech launching the report today, Dr Horne said: ‘It is clear that our nation is living through a moment that, in hindsight, we will see as one of enormous consequence.
‘A “sliding doors” moment. A moment of choice. In the coming months, we face a real prospect of an unprecedented rise in the number of cyber-incidents.
‘But we must be clear that is not because AI has invented new ways to attack us, but because vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale that was once unimaginable.’
His intervention came just days after Defence Secretary Wes Streeting warned Britain must be ready for war within the next 1,000 days.
At the same time, the Government launched a new resilience drive, urging Britons to stockpile enough food and water for three days.
Dr Horne added: ‘For decades, we have collectively got away with doing tech on the cheap.
‘End-of-life systems kept running for just one more year, well-needed upgrades pushed back as a “cost efficiency”, and technology providers failing to invest in security by design and default.’
The NCSC annual report said its incident management team received 1,831 reports of cyber attacks this year, of which 337 required support and 80 were nationally significant.
It also warned that 8,500 organisations when their systems had been compromised by attackers, the report added.
Almost half of small firms in the UK (46 per cent) have been targeted by cyber criminals in the past year, with nearly one in five (18 per cent) going bankrupt following a cyber attack, according to research by Mastercard.
The study added that more than three in five small to medium-sized companies – about 3.4million – in the UK did not use any cyber-security tools.


Leave a comment